Log inSign up
Log inSign up
elceef
543 posts
elceef profile banner
@elceef

elceef

@elceef
Security Researcher. Threat Hunter. Chocolate Junkie.
Central Europe
github.com/elceef
Joined January 2013
222 Following
868 Followers
RepliesRepliesRepostsRepostsMediaMedia

Log in or sign up for X

See what’s happening and join the conversation

Continue with phone
or
Log in with username or email
Terms·Privacy·Cookies·Accessibility·US TIDA·Ads Info·© 2026 X Corp.
  • @elceef
    elceef
    @elceef
    Dec 22, 2024
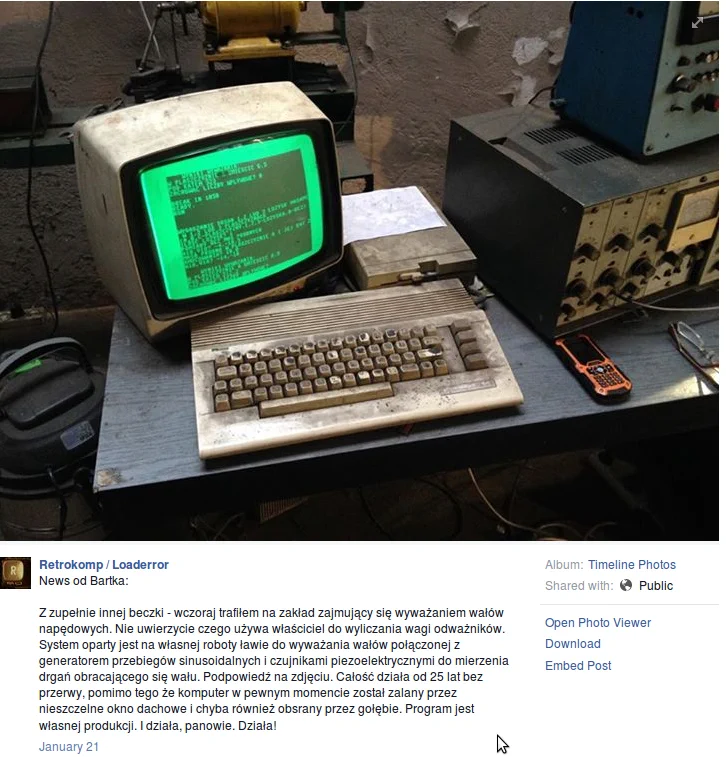
    Auto repair shop in Gdańsk, Poland uses a Commodore 64 running self-made program for balancing driveshafts. It's been working non-stop for over 25 years despite a flood, omnipresent dust and pigeons.
  • @elceef
    elceef
    @elceef
    Aug 24, 2023
    This YARA rule might be helpful: github.com/elceef/yara-ru…
    @GroupIB_TI
    Group-IB Threat Intelligence
    @GroupIB_TI
    Aug 23, 2023
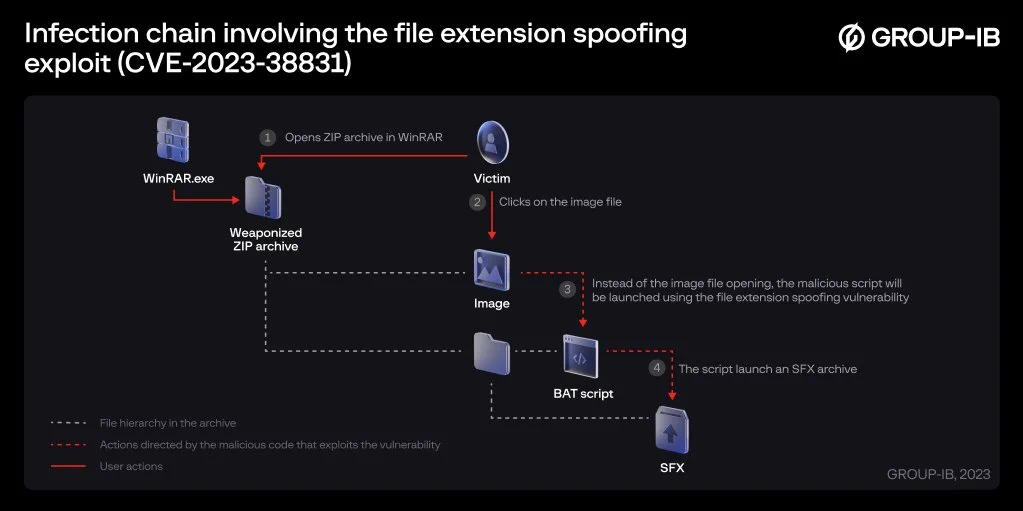
    ⚡️Group-IB Threat intelligence discovers a new 0-day in #WinRAR used to target traders #CVE-2023-38831 allows TAs to spoof file extensions and hide the launch of malicious script within a ZIP archive masquerading as a '.jpg', '.txt', and other formats ➡️bit.ly/45fFq44
  • @elceef
    elceef
    @elceef
    Jun 5, 2023
    Heavily obfuscated batch scripts detected with #YARA rule BAT_Begin_Substring_Env: github.com/elceef/yara-ru…
    @LevelBlueCyber
    LevelBlue
    @LevelBlueCyber
    May 31, 2023
    A hooded, faceless figure is sitting behind a computer screen with a shield graphic superimposed on the computer connecting to additional icons such as email, cell phone, and other images denoting that the person is hacking into someone's network and accessing their personal information.
    Our latest threat analysis explores the rise of Remote Access Trojan (RAT) SeroXen to help teams identify and help protect against the pervasive threat. From execution analysis to detection methods, read our latest blog to learn more about the malware: cybersecurity.att.com/blogs/labs-res…
  • @elceef
    elceef
    @elceef
    May 11, 2023
    Updated YARA rule Outlook_CVE_2023_23397_Exploit github.com/elceef/yara-ru…
    @akamai_research
    Akamai Security Intelligence Group
    @akamai_research
    May 10, 2023
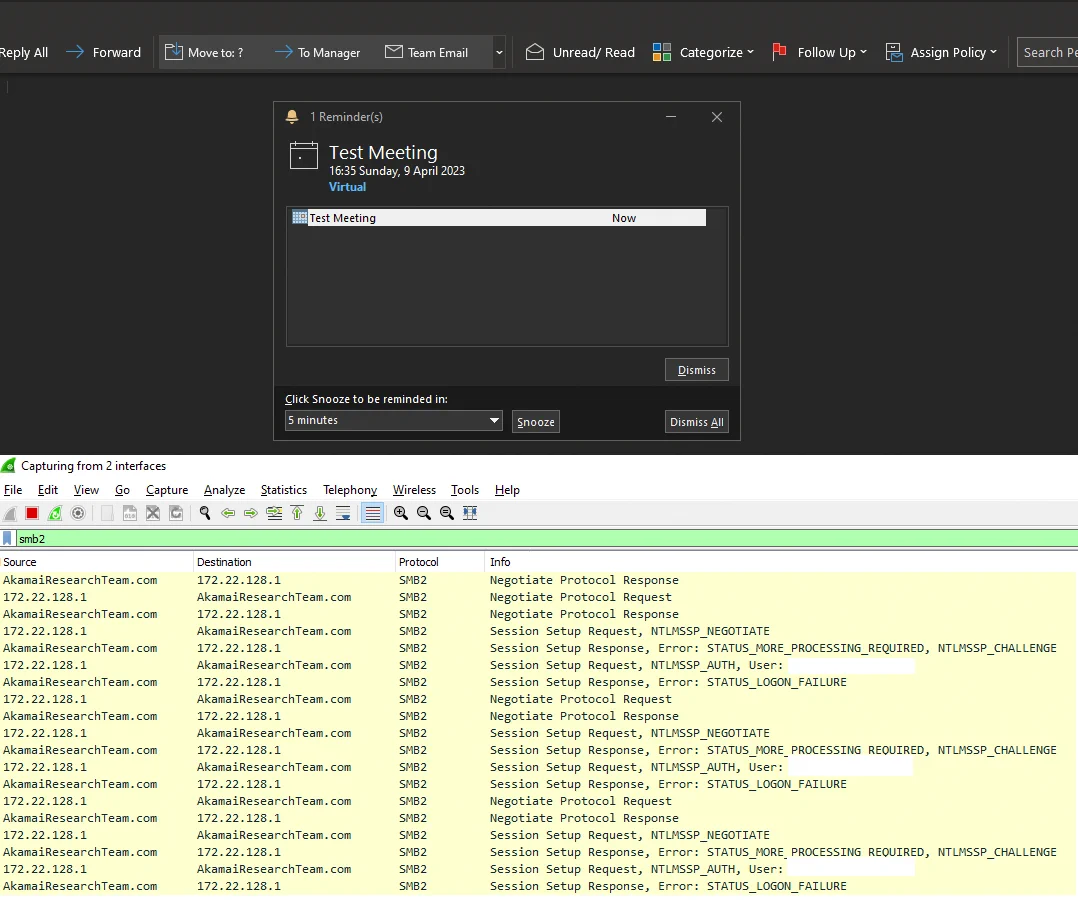
    Remember that 0-click Outlook vulnerability with a custom sound leading to NTLM theft? Akamai researchers found a way to bypass the patch to it. In our write-up, see how adding a slash allowed for a bypass. akamai.com/blog/security-…
    Triggering the calendar event, leading to NTLM authentication against a remote server
  • @elceef
    elceef
    @elceef
    May 9, 2023
    dnstwist 20230509 is out! This update provides more precise homograph permutations for selected country-code TLDs. github.com/elceef/dnstwist