Log inSign up
Log inSign up
Sandfly Security
751 posts
Sandfly Security profile banner
@SandflySecurity

Sandfly Security

@SandflySecurity
Agentless Linux security. We post threat hunting, DFIR and hardening for people running Linux in production. No agents, no kernel modules.
Christchurch, New Zealand
sandflysecurity.com
Joined March 2017
53 Following
2,991 Followers
RepliesRepliesRepostsRepostsMediaMediaArticlesArticles

Log in or sign up for X

See what’s happening and join the conversation

Continue with phone
or
Log in with username or email
Terms·Privacy·Cookies·Accessibility·US TIDA·Ads Info·© 2026 X Corp.
  • @SandflySecurity
    Sandfly Security
    @SandflySecurity
    Oct 8
    A Linux process running with an immutable binary is almost never legitimate. Attackers set the immutable flag so you can't delete their payload mid-incident. It’s a huge red flag that a system is compromised. ap1.hubs.ly/H01kJD10 #Linux #eBPF
    2
  • @SandflySecurity
    Sandfly Security
    @SandflySecurity
    Oct 7
    A global automotive manufacturer runs its assembly lines and AGVs on Linux. Downtime costs thousands a minute. Agent-based tools kept causing problems on exactly those systems. So they stopped using them. ap1.hubs.ly/H01qdR-0 #ThreatHunting #Linux
    Automotive Manufacturing Chooses Agentless Linux EDR After Agent-Based Failures
    From sandflysecurity.com
  • @SandflySecurity
    Sandfly Security
    @SandflySecurity
    Oct 6
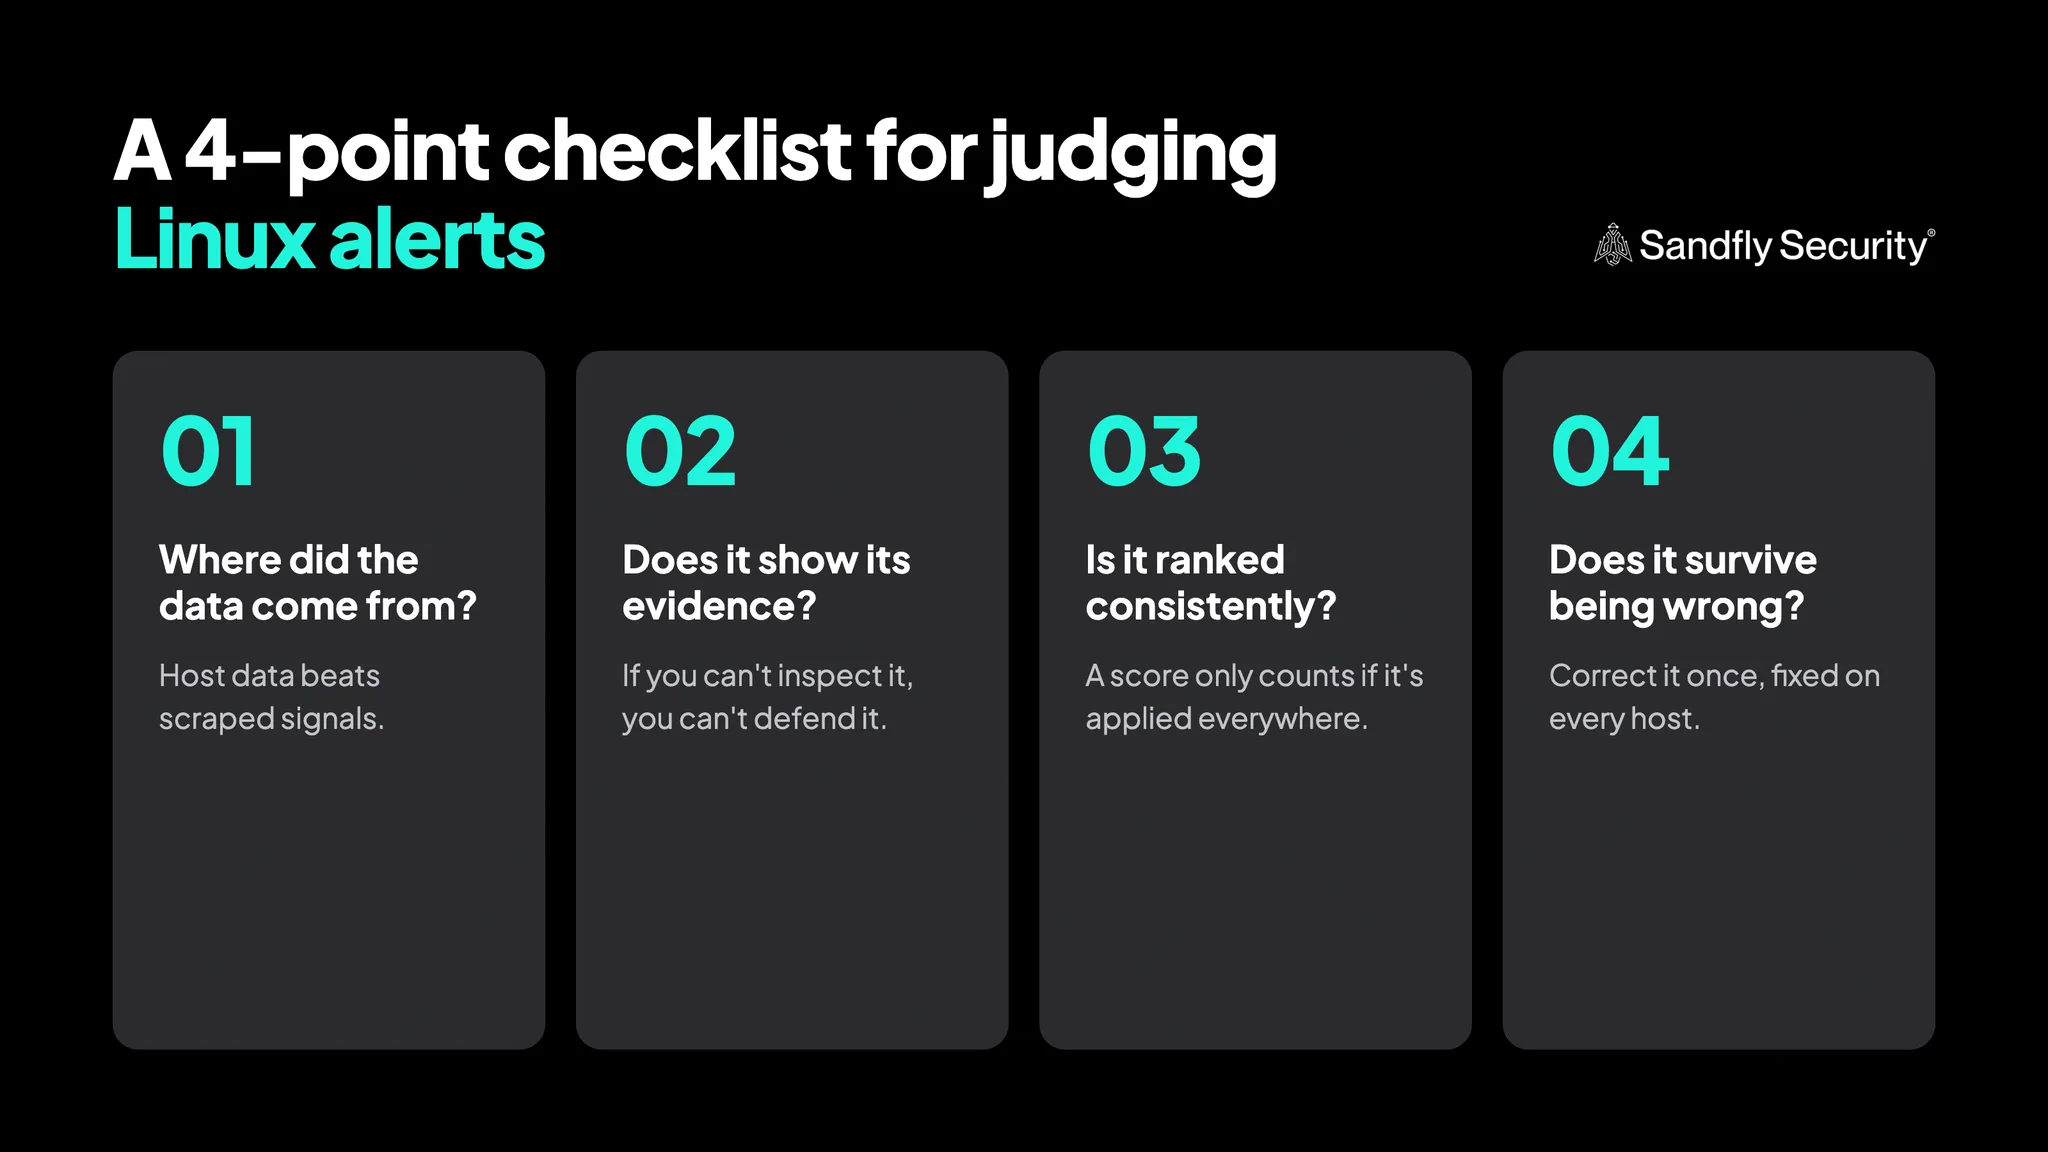
    Most Linux alerts aren't worth your time. A few are worth everything 👀 The hard part is telling which is which. On Tue 27 Oct, Sandfly founder Craig Rowland shares 4 questions to ask before you act on any detection. Free. ap1.hubs.ly/H01qdRl0
  • @SandflySecurity
    Sandfly Security
    @SandflySecurity
    Oct 4
    Attackers are encrypting payloads to sneak malware past Linux defenses. Spoiler: it doesn't work.Sandfly Founder, @CraigHRowland breaks down the Linux malware trends we're seeing on @DestLinuxPod 👇
    @CraigHRowland
    Craig H. Rowland
    @CraigHRowland
    Oct 3
    In this episode I go over some emerging Linux malware trends we saw resurface around memfd fileless loading. The twist is it uses an encrypted payload to try to evade detection (no, it doesn't evade). Also I go over other trends we're seeing in Linux malware.
    Quote
    @DestLinuxPod
    Destination Linux
    @DestLinuxPod
    Sep 28
    A new #DestinationLinux! 😂💖🐧🐧🐧 youtu.be/LkWJ_yvhKwo Cold Incident Response Conference, OpenRGB Adds Support for New Hardware, Peppermint OS Moving to XLibre, Ubuntu 26.10 update, MX Linux DDoS Attack #Linux #podcast Thank you @SandflySecurity! sandflysecurity.com/?utm_source=d...
  • @SandflySecurity
    Sandfly Security
    @SandflySecurity
    Oct 3
    In this episode we discuss some emerging Linux malware trends we're seeing in the wild leveraging fileless encrypted payloads.
    @DestLinuxPod
    Destination Linux
    @DestLinuxPod
    Sep 28
    A new #DestinationLinux! 😂💖🐧🐧🐧 youtu.be/LkWJ_yvhKwo Cold Incident Response Conference, OpenRGB Adds Support for New Hardware, Peppermint OS Moving to XLibre, Ubuntu 26.10 update, MX Linux DDoS Attack #Linux #podcast Thank you @SandflySecurity! sandflysecurity.com/?utm_source=d...