Log inSign up
Log inSign up
Oliver Lyak
116 posts
Oliver Lyak profile banner
@ly4k_

Oliver Lyak

@ly4k_
Yet another security researcher 🔦 Github: github.com/ly4k
Copenhagen, Denmark
medium.com/@oliverlyak
Joined March 2014
268 Following
8,744 Followers
RepliesRepliesRepostsRepostsMediaMedia

Log in or sign up for X

See what’s happening and join the conversation

Continue with phone
or
Log in with username or email
Terms·Privacy·Cookies·Accessibility·US TIDA·Ads Info·© 2026 X Corp.
  • Pinned
    @ly4k_
    Oliver Lyak
    @ly4k_
    May 15, 2025
    👇
    The Future of Certipy and the Release of v5 & ESC16 · ly4k Certipy · Discussion #270
    From github.com
    16
  • @ly4k_
    Oliver Lyak
    @ly4k_
    Dec 26, 2022
    Today we're publishing new techniques for recovering NTLM hashes from encrypted credentials protected by Windows Defender Credential Guard. These techniques also work on victims logged on before the server was compromised.
    Pass-the-Challenge: Defeating Windows Defender Credential Guard
    From research.ifcr.dk
    34
  • @ly4k_
    Oliver Lyak
    @ly4k_
    Aug 4, 2022
    Certipy reached 1k stars on GitHub. Let’s celebrate with a brand new version, new research, a forked BloodHound GUI with ADCS support, and many new features, for instance Schannel authentication via LDAPS, SSPI authentication, and much more!
    Certipy 4.0: ESC9 & ESC10, BloodHound GUI, New Authentication and Request Methods — and more!
    From research.ifcr.dk
    18
  • @ly4k_
    Oliver Lyak
    @ly4k_
    May 10, 2022
    The first blog post is here. This one covers the technical details of CVE-2022-26923 (Active Directory Domain Services Elevation of Privilege Vulnerability). The vulnerability was patched as part of the May 2022 Security Updates from Microsoft. research.ifcr.dk/9e098fe298f4
    25
  • @ly4k_
    Oliver Lyak
    @ly4k_
    May 10, 2022
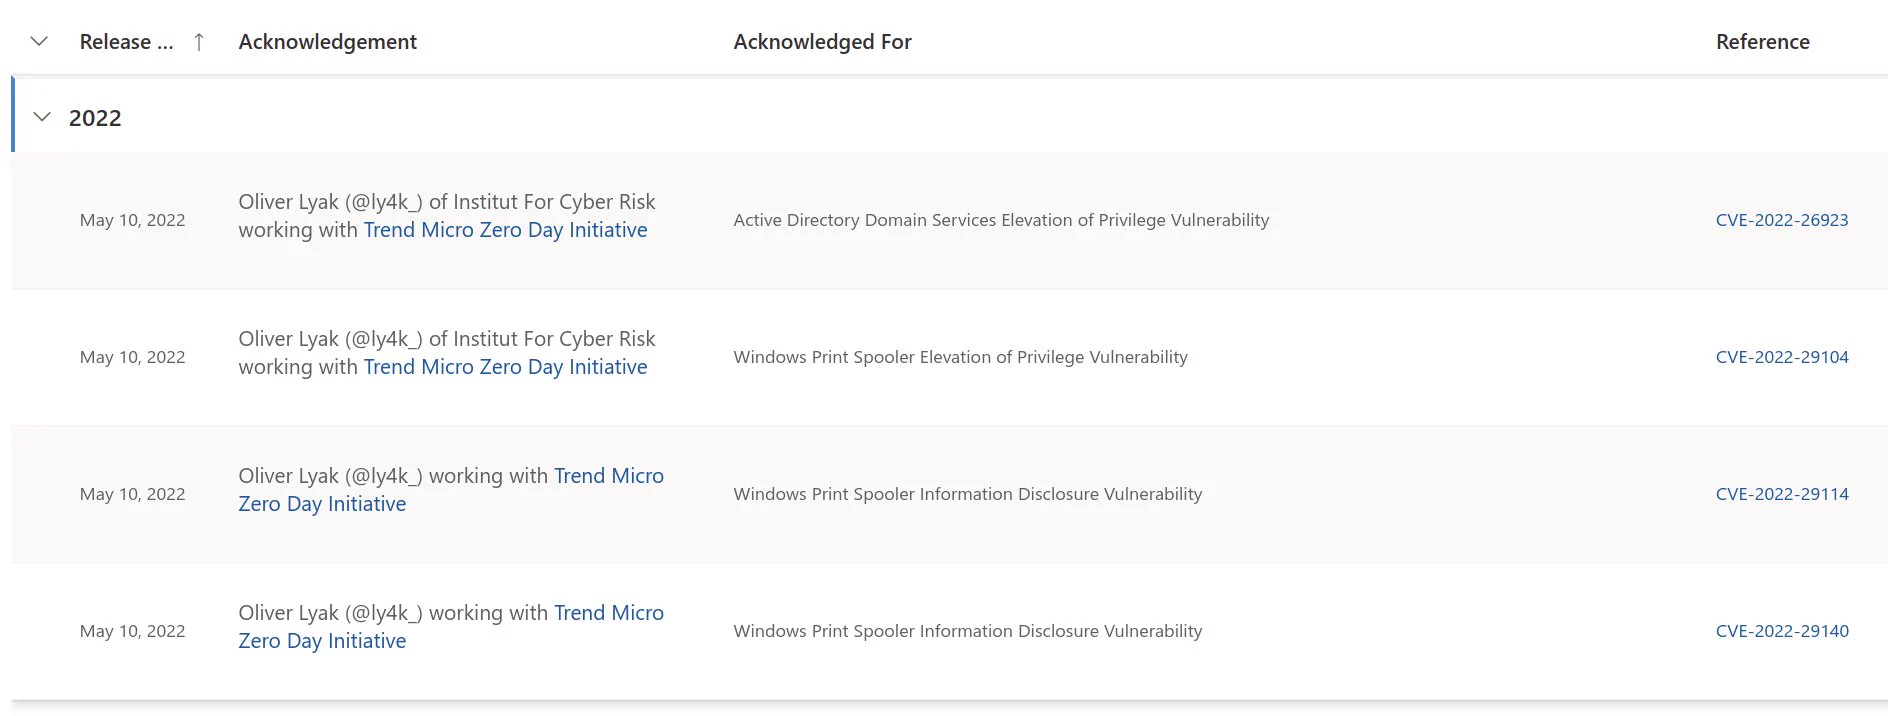
    Happy Patch Tuesday! Today, Microsoft patched a series of vulnerabilities that I reported a while ago. 1 is a critical Active Directory privilege escalation, and 3 are Print Spooler vulnerabilities, including a local privilege escalation. Stay tuned for the technical details.
    1