Repository navigation
fix: title bar resizing in north direction - #455
Merged
Merged
Conversation


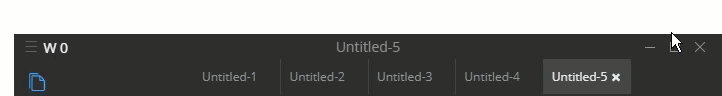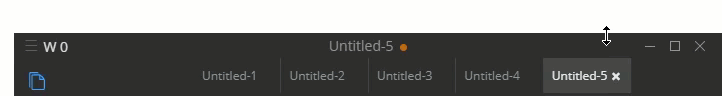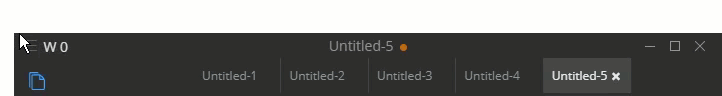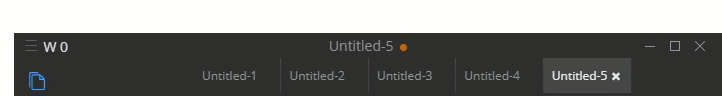
Fixing window resizing in north direction
Added title-no-drag to left-toolbar for non darwin systems

fxha
approved these changes
Aug 9, 2018

Jocs
approved these changes
Aug 12, 2018


Member
|
@mdogadailo thanks! |

Jocs
added a commit
that referenced
this pull request
Jun 21, 2026

* chore(deps): bump dompurify to ^3.4.9 across desktop/muya/muyajs

Updates the HTML sanitizer from ^3.4.3/^3.4.5 to ^3.4.9 (resolves to
3.4.11), deduping the two installed versions (3.4.3 + 3.4.7) into one.
Clears Dependabot alerts #443/#451/#452/#453/#454/#455/#456.

MarkText calls DOMPurify.sanitize() only with string input and
RETURN_TRUSTED_TYPE: false (no IN_PLACE/RETURN_DOM/addHook/
SAFE_FOR_TEMPLATES), so none of these CVEs were reachable; the bump is
defense-in-depth for the editor's HTML sanitization path.

DOMPurify 3.4.8+ hardened cross-realm namespace validation, which the
happy-dom test environment does not satisfy: under happy-dom it strips
every element, even default-allowed tags like <p>/<h1>. Real
Chromium/Electron is unaffected (verified: jsdom, which matches production
DOM behavior, sanitizes correctly). Move the five DOMPurify-dependent muya
specs to the jsdom environment and declare jsdom as a muya devDependency.

Co-Authored-By: Claude Opus 4.8 (1M context) <[email protected]>

* chore(deps): bump happy-dom to ^20.8.9 in muya

Updates muya's vitest DOM test environment from ^15.11.7 to ^20.8.9
(resolves to 20.10.6). Clears Dependabot alerts
#426/#427/#428/#434/#437/#438 (2 critical "VM context escape / RCE",
4 high).

happy-dom is a devDependency used only as the unit-test DOM; it is never
bundled into the shipped app, and the muya suites run trusted fixtures, so
these CVEs were not reachable. The bump keeps the test toolchain current and
clears the critical badges. The full muya unit suite (143 files) passes on
20.x — the DOMPurify-dependent specs already moved to jsdom in the previous
commit.

Co-Authored-By: Claude Opus 4.8 (1M context) <[email protected]>

* chore(deps): update vite to patched 7.3.5 / 8.0.16

Bumps vite to the patched releases across the workspace (desktop ^7.3.5,
muya + muya-e2e ^8.0.16), updating the declared floors so installs can't
regress below the fix. Clears Dependabot alerts #441/#442/#447/#448
(server.fs.deny bypass + launch-editor NTLMv2 disclosure — both Windows
dev-server only; vite is build tooling, never shipped to users).

Co-Authored-By: Claude Opus 4.8 (1M context) <[email protected]>

* chore(deps): pin transitive deps to patched versions via pnpm overrides

Adds range-scoped pnpm.overrides to force patched releases of the transitive
dependencies Dependabot flagged, while leaving unaffected older majors in
place (undici 6.x, esbuild 0.25.x, js-yaml 3.x):

  form-data   4.0.5      -> 4.0.6   (#450 CRLF injection)
  tmp         0.2.5      -> 0.2.6   (#411 path traversal)
  tar         7.5.15     -> 7.5.16  (#449 PAX file smuggling)
  ws          8.20.1     -> 8.21.0  (#444 memory-exhaustion DoS)
  undici      7.24/7.25  -> 7.28.0  (#457 SOCKS5 TLS bypass; keeps 6.25.0)
  esbuild     0.27/0.28.0-> 0.28.1  (#439 dev-server file read; keeps 0.25.x)
  @babel/core 7.29.0     -> 7.29.6  (#445 sourceMappingURL file read)
  js-yaml     4.1.1      -> 4.2.0   (#446 merge-key DoS; keeps 3.14.2)

All are build/test/website tooling reachable only on developer/CI machines,
never bundled into the shipped app. js-yaml 3.14.2 remains via the website's
gray-matter (no 3.x patch exists); it parses only trusted first-party
content, so #446 is not exploitable there and will be dismissed on GitHub.

Co-Authored-By: Claude Opus 4.8 (1M context) <[email protected]>

---------

Co-authored-by: Claude Opus 4.8 (1M context) <[email protected]>
thimbleberrysystems
pushed a commit
to thimbleberrysystems/WordBird
that referenced
this pull request
Jun 21, 2026

Fixing window resizing in north direction
Added title-no-drag to left-toolbar for non darwin systems
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
3 participants


Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Description
Fixing window resizing in north direction on top of title bar.
Added title-no-drag to left-toolbar for non darwin systems